 Sync
Cryptographic Security & 38+ Cloud Connectors
SyncMage is built on a strict separation between account authentication and background data transfer, ensuring your cloud credentials remain encrypted and your files are never permanently stored on our servers.
Every security guarantee on this page and in our privacy policy is enforced by default across all connected services.
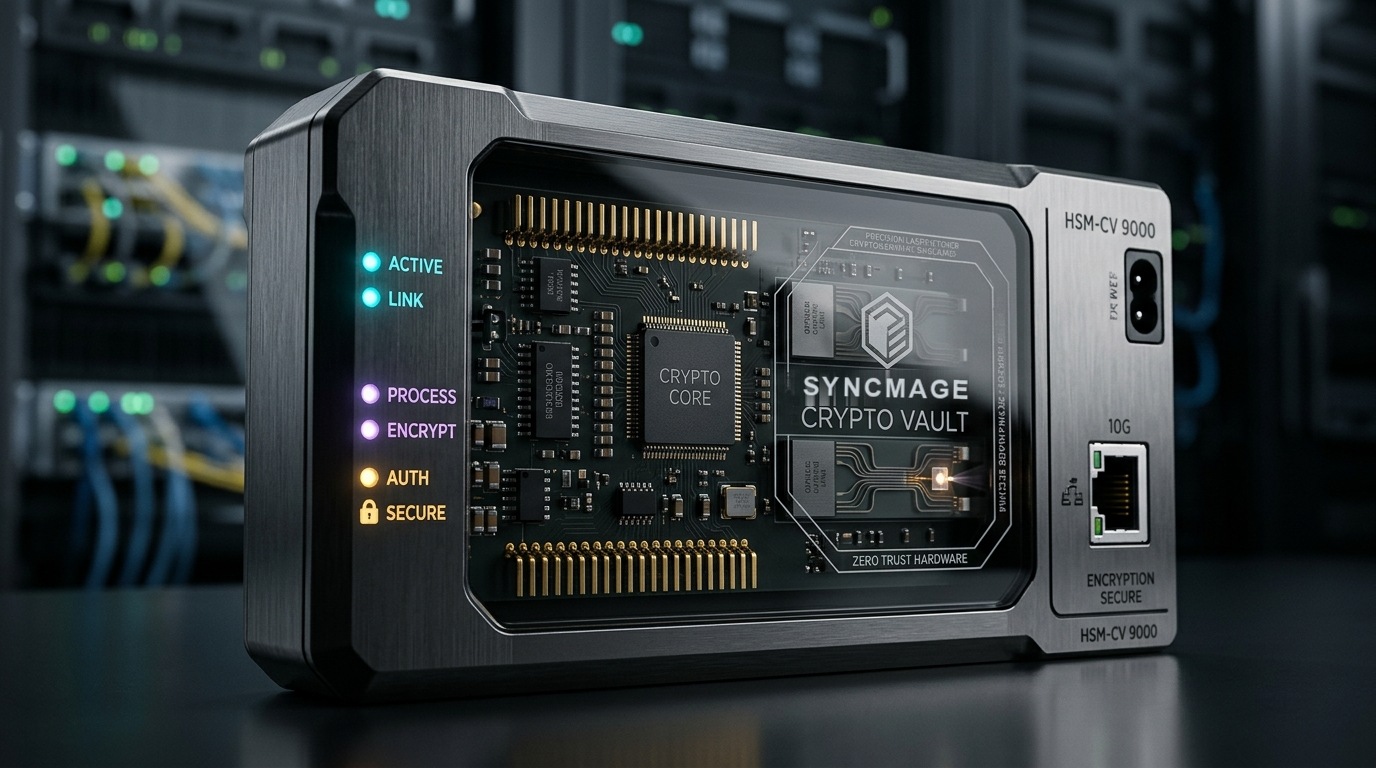
Isolated Account & Transfer Layers
Your account settings, cloud connections, and background file transfers run in separate, protected layers over a private network.
Protected Sign-In & 2FA
Protects your account with strong password encryption, two-factor authentication (2FA), active device session controls, and folder permissions for team sub-accounts.
Private File Transfer Spaces
Runs background cloud transfers, sync tasks, versioned backups, and email-to-PDF archiving in isolated workers that are never exposed to the public internet.
Signed Internal Communication
Every instruction between your dashboard and the transfer engine is digitally verified so unauthorized commands can never run.
Automatic 24h Cache Cleanup
Direct cloud transfers bypass local storage entirely. When temporary conversion is needed, data is encrypted, deleted as soon as the task finishes, and automatically wiped within 24 hours.
How Tokens and User Data Are Protected
AES-256-GCM Token Vault & Key Rotation
OAuth tokens and provider credentials are encrypted with AES-256-GCM and unlocked only in memory for the duration of an active task. Seamless encryption key rotation is supported without interrupting connected accounts.
Automatic Log Redaction & Network Guards
System logs automatically redact access tokens, refresh tokens, passwords, and authorization headers. Remote URL and server connectors block private internal IP ranges to prevent unauthorized network probing.
Instant Revocation & 14-Day Full Purge
Disconnecting a cloud account immediately revokes the OAuth token at the provider and deletes it from our vault. Deleting your SyncMage account removes all account records and task history within 14 days (see deletion policy).
Unified 38+ Cloud Connector Ecosystem
Every connected service uses a unified cloud adapter that enforces least-privilege permissions, automatic rate-limit backoff, and consistent checksum verification across personal drives, enterprise suites, object storage, and mailboxes.
| Category | Providers & Protocols | Capabilities & Security Highlights |
|---|---|---|
| Personal Cloud Storage | Google Drive, OneDrive, Dropbox, Box, pCloud, MEGA, Yandex Disk, HiDrive, SugarSync, Jottacloud, Koofr | In-memory token handling, real-time change feed detection (Drive Changes, OneDrive Delta, Dropbox Longpoll), and native server-side copy. |
| S3 & Object Storage | Amazon S3, Wasabi, Cloudflare R2, DigitalOcean Spaces, MinIO, IDrive e2, Backblaze B2 | High-throughput multipart streaming, bucket-level root scoping, presigned URL generation, and MD5/SHA-1 integrity checks. |
| Enterprise & Team Suites | Google Workspace, Shared Drives, OneDrive for Business, SharePoint Online, Dropbox Business, Box for Business, Egnyte | Organization member discovery, verified Google Workspace Domain-Wide Delegation, and SharePoint site/document library browsing. |
| Mail & Photo Services | Gmail, Microsoft Outlook, Google Photos (Picker API), iCloud Photos, Flickr | Gmail & Outlook connect strictly in read-only mode for Email-to-PDF archiving; Google Photos uses Google's official Picker session flow. |
| Server & Specialized Protocols | FTP / FTPS, SFTP, WebDAV (Nextcloud, ownCloud), SMB / NAS, MySQL, MediaFire, Evernote, Icedrive, 4shared | Streaming SFTP + database website backups, Evernote notebook export with attachments, and encrypted credential handling. |